The biggest GDPR fine ever issued is EUR 1.2 billion, imposed on Meta Platforms Ireland Limited by Ireland’s Data Protection Commission in May 2023 for sending EU user data to the United States without a valid legal mechanism. The 50 biggest GDPR fines now add up to about EUR 7.0 billion, and the list changed in 2026: Uber’s EUR 824.99 million fine is second and Google’s EUR 403 million fine is fifth. Last updated 13 November 2026, per the CMS Enforcement Tracker and regulator announcements.
What is the biggest GDPR fine ever?
The record fine is EUR 1.2 billion, issued by Ireland’s Data Protection Commission against Meta Platforms Ireland Limited on 22 May 2023. It followed a binding decision from the European Data Protection Board and concerned Meta’s transfers of EU user data to the US after the Court of Justice of the EU struck down the Privacy Shield framework. Meta has appealed, and the appeal is still pending as of November 2026.
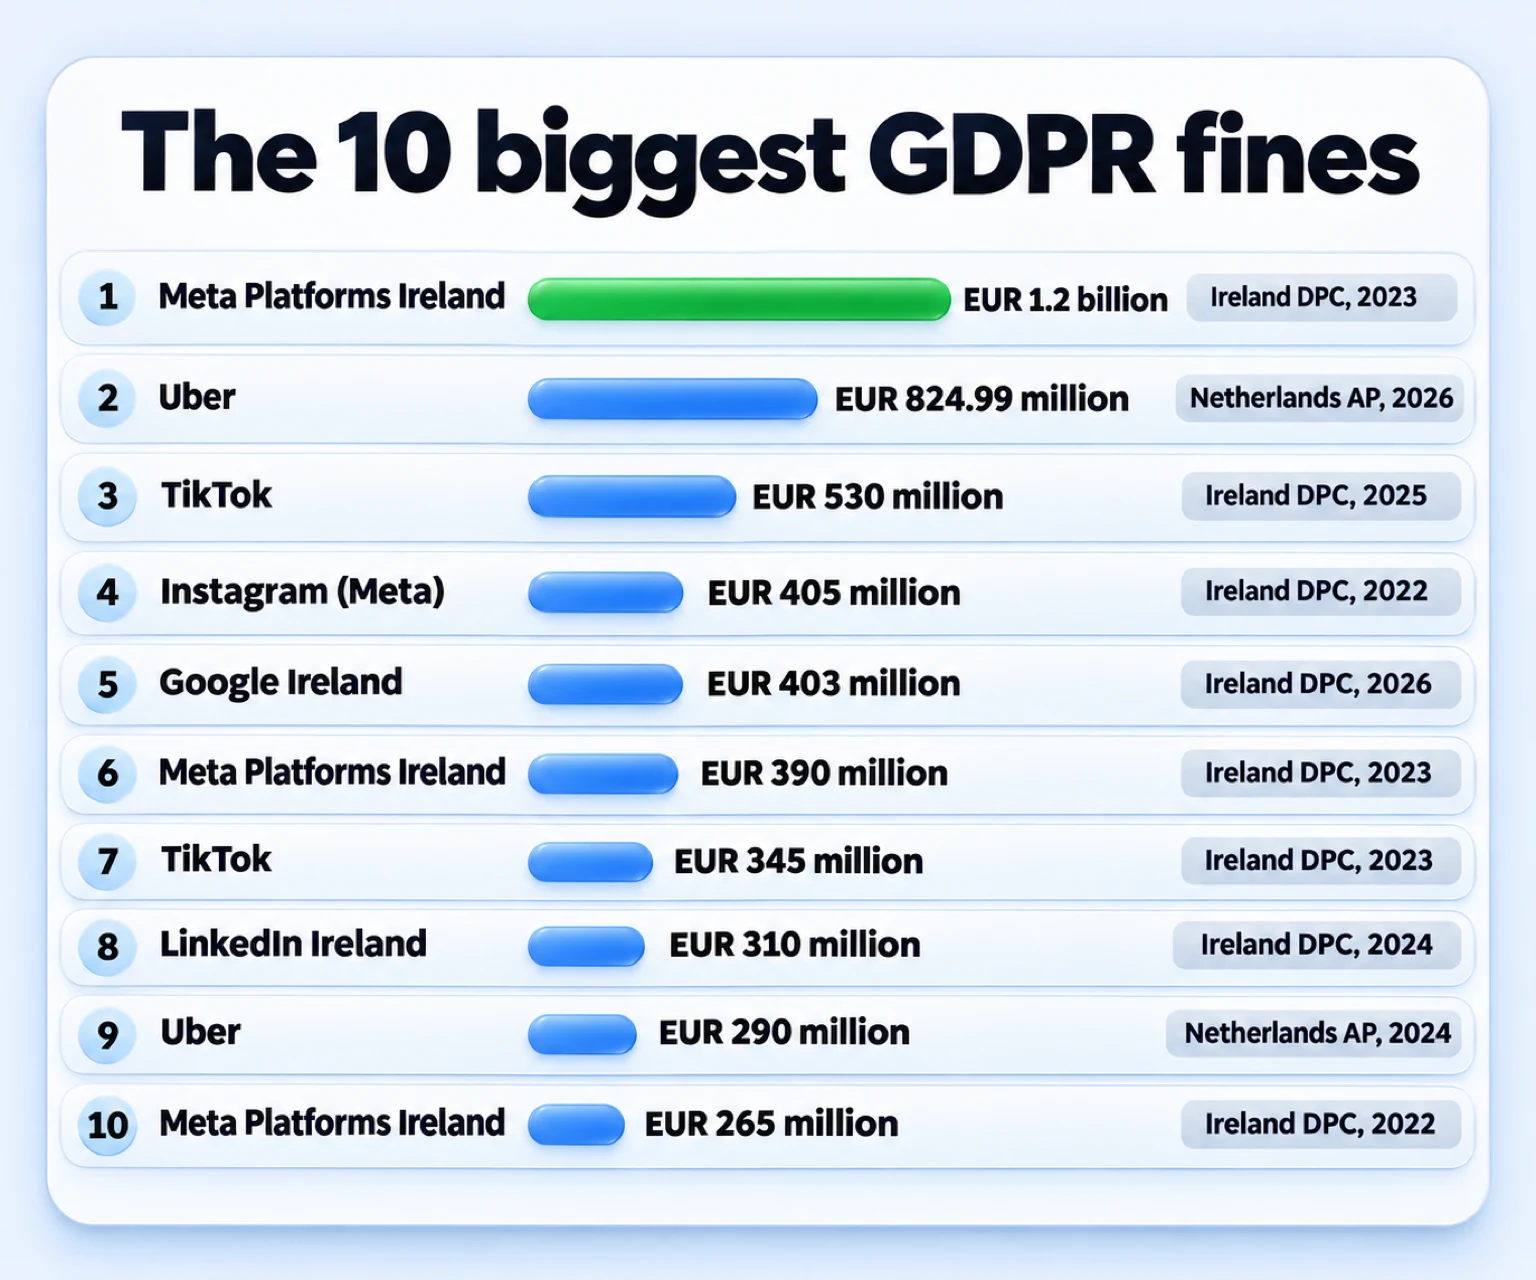
The fine is about 45% larger than the second-biggest, Uber’s EUR 824.99 million penalty from the Dutch Autoriteit Persoonsgegevens, and more than double the third-place EUR 530 million fine against TikTok. In 2026 alone two new fines entered the top 10, yet none came close to displacing Meta: the nearest challenger fell EUR 375 million short. For the full chronology see our GDPR fines timeline, and for the Meta cases in isolation see how much Meta has paid in GDPR fines.
One-line takeaway: the record has stood for more than three years and the only fine to get within EUR 400 million of it was issued in August 2026.
Figure 1: The 5 largest GDPR fines by amount in force. Source: DPC Ireland, Dutch Autoriteit Persoonsgegevens, CMS Enforcement Tracker, checked 13 November 2026.
The 50 biggest GDPR fines, ranked by amount
The table below lists the 50 biggest GDPR fines in force, from EUR 1.2 billion down to EUR 9.5 million. Sixteen of them are EUR 100 million or more. Amounts are in millions of euros, dates are the month of the regulator’s decision or announcement, and status is as of 13 November 2026. Fines from the UK Information Commissioner are shown in euros as converted by the tracker, with the pound figure in the reason column.
| Rank | Company | Fine (EUR M) | Regulator, date | Articles, reason and status |
|---|---|---|---|---|
| 1 | Meta Platforms Ireland | 1,200.00 | Ireland DPC, May 2023 | Art. 46(1). Transfers of EU user data to the US without a valid mechanism. Appealed. |
| 2 | Uber Technologies | 824.99 | Netherlands AP, Aug 2026 | Art. 22, 13. Solely automated driver deactivations; too little information on profiling. Appealed. |
| 3 | TikTok Technology | 530.00 | Ireland DPC, May 2025 | Art. 46(1), 13(1)(f). Transfers of EU user data to China. Appealed (stay granted). |
| 4 | Instagram (Meta) | 405.00 | Ireland DPC, Sep 2022 | Art. 5, 6, 12, 24, 25, 35. Children’s contact details public by default. Appealed. |
| 5 | Google Ireland | 403.00 | Ireland DPC, Sep 2026 | Art. 5, 6, 12, 13. Location data: Web & App Activity, Location History. Appealed (judicial review). |
| 6 | Meta Platforms Ireland | 390.00 | Ireland DPC, Jan 2023 | Art. 5(1)(a), 6, 12, 13. Contract as legal basis for behavioral ads. Appealed. |
| 7 | TikTok | 345.00 | Ireland DPC, Sep 2023 | Art. 5, 12, 13, 24, 25. Children’s accounts public by default. Appealed. |
| 8 | LinkedIn Ireland | 310.00 | Ireland DPC, Oct 2024 | Art. 5, 6, 13, 14. Invalid consent and legitimate interests for ad targeting. Appealed. |
| 9 | Uber Technologies | 290.00 | Netherlands AP, Aug 2024 | Art. 44. Driver data sent to the US without safeguards. Appealed. |
| 10 | Meta Platforms Ireland | 265.00 | Ireland DPC, Nov 2022 | Art. 25(1), (2). Data-scraping breach, privacy by design. Appealed. |
| 11 | Meta Platforms Ireland | 251.00 | Ireland DPC, Dec 2024 | Art. 33, 25. 2018 ‘View As’ security breach. Appealed. |
| 12 | WhatsApp Ireland | 225.00 | Ireland DPC, Sep 2021 | Art. 5, 12, 13, 14. Transparency about sharing with Meta companies. Appealed. |
| 13 | Google LLC | 200.00 | France CNIL, Sep 2025 | Art. 82 LIL, L.34-5 CPCE. Gmail ads and cookies without consent. No change reported. |
| 14 | Shein (Infinite Styles Services) | 150.00 | France CNIL, Sep 2025 | Art. 82 LIL. Cookies placed without consent. Appeal announced. |
| 15 | Google Ireland | 125.00 | France CNIL, Sep 2025 | Art. 82 LIL, L.34-5 CPCE. Gmail ads and cookies without consent. No change reported. |
| 16 | Ridetech International (Yango) | 100.00 | Netherlands AP, Apr 2026 | Art. 5, 44, 46. Rider and driver data stored in Russia. No change reported. |
| 17 | Meta Platforms Ireland | 91.00 | Ireland DPC, Sep 2024 | Art. 5(1)(f), 32, 33. Passwords stored in plain text. Appealed. |
| 18 | Google LLC | 90.00 | France CNIL, Dec 2021 | Art. 82 LIL. Cookie refusal harder than acceptance. No change reported. |
| 19 | Enel Energia | 79.10 | Italy Garante, Feb 2024 | Art. 5, 24, 25, 28, 32. Telemarketing with unlawful contact lists. No change reported. |
| 20 | Google Ireland | 60.00 | France CNIL, Dec 2021 | Art. 82 LIL. Cookie refusal harder than acceptance. No change reported. |
| 21 | Facebook Ireland | 60.00 | France CNIL, Dec 2021 | Art. 82 LIL. Cookie refusal harder than acceptance. No change reported. |
| 22 | Google LLC | 50.00 | France CNIL, Jan 2019 | Art. 5, 6, 13, 14. Transparency and ad consent. No change reported. |
| 23 | Vodafone GmbH | 45.00 | Germany BfDI, Jun 2025 | Art. 28(1), 32. Partner-agency fraud and weak authentication. Accepted by company. |
| 24 | Criteo | 40.00 | France CNIL, Jun 2023 | Art. 7, 12, 13, 15, 17, 26. No proof of consent for ad tracking. No change reported. |
| 25 | H&M Online Shop | 35.26 | Hamburg DPA, Oct 2020 | Art. 5, 6. Excessive employee surveillance. No change reported. |
| 26 | Intesa Sanpaolo | 31.80 | Italy Garante, Mar 2026 | Art. 5, 24, 32, 33, 34. Insider access to client accounts. No change reported. |
| 27 | Clearview AI | 30.50 | Netherlands AP, Sep 2024 | Art. 5, 6, 9, 12, 14, 27. Facial-recognition database scraped from the web. No change reported. |
| 28 | TIM | 27.80 | Italy Garante, Jan 2020 | Art. 5, 6, 17, 21, 32. Unsolicited marketing calls. No change reported. |
| 29 | Free Mobile | 27.00 | France CNIL, Jan 2026 | Art. 5(1)(e), 32. 2024 breach of 24 million subscribers. No change reported. |
| 30 | British Airways | 22.05 | UK ICO, Oct 2020 | Art. 5(1)(f), 32. 2018 breach, 400,000+ customers (GBP 20M). Reduced from GBP 183M proposed. |
| 31 | Marriott International | 20.45 | UK ICO, Oct 2020 | Art. 32. 2014 breach (GBP 18.4M). Reduced from GBP 99M proposed. |
| 32 | Clearview AI | 20.00 | Italy Garante, Feb 2022 | Art. 5, 6, 9, 12-15, 27. Biometric scraping without legal basis. No change reported. |
| 33 | Clearview AI | 20.00 | Greece HDPA, Jul 2022 | Art. 5, 6, 9, 12, 14, 15, 27. Biometric scraping without legal basis. No change reported. |
| 34 | Clearview AI | 20.00 | France CNIL, Oct 2022 | Art. 6, 12, 15, 17, 31. Biometric scraping; rights ignored. No change reported. |
| 35 | Intesa Sanpaolo | 17.63 | Italy Garante, Mar 2026 | Art. 6, 13. Profiling 2.4M customers for Isybank move. No change reported. |
| 36 | Meta Platforms Ireland | 17.00 | Ireland DPC, Mar 2022 | Art. 5(2), 24(1). 12 breach notifications, security measures. No change reported. |
| 37 | Wind Tre | 16.70 | Italy Garante, Jul 2020 | Art. 5, 6, 12, 24, 25. Telemarketing without consent. No change reported. |
| 38 | 16.61 | UK ICO, Feb 2026 | Art. 5, 6, 8, 35. Children’s data (GBP 14.47M). No change reported. | |
| 39 | Austrian Post | 16.00 | Austria DSB, Oct 2019 | Art. 5, 6. Political-affinity profiling (court-set, not final). Reduced from EUR 18M. |
| 40 | Amazon France Logistique | 15.00 | France CNIL, Jan 2024 | Art. 5, 6, 12, 13, 32. Warehouse worker monitoring. Reduced from EUR 32M. |
| 41 | Free | 15.00 | France CNIL, Jan 2026 | Art. 32, 34. 2024 breach of 24 million subscribers. No change reported. |
| 42 | TikTok | 14.50 | UK ICO, Apr 2023 | Art. 5, 12, 13. Under-13s’ data (GBP 12.7M). No change reported. |
| 43 | Amadeus IT Group | 14.40 | Spain AEPD, May 2026 | Art. 6, 14. Traveler profiling pilot without legal basis or notice (EUR 18M cut 20% for early payment). Company says it will contest. |
| 44 | Avast Software | 13.90 | Czech UOOU, Apr 2024 | Articles not published. Browser data sold through Jumpshot. No change reported. |
| 45 | Vodafone Italia | 12.25 | Italy Garante, Nov 2020 | Art. 5, 6, 7, 15-25, 32. Telemarketing and consent failures. No change reported. |
| 46 | Aena | 10.04 | Spain AEPD, Nov 2025 | Art. 35. Airport facial recognition without a valid impact assessment. Appeal announced. |
| 47 | Google LLC | 10.00 | Spain AEPD, May 2022 | Art. 6, 17. Data shared with Lumen; erasure. No change reported. |
| 48 | Axpo Italia | 10.00 | Italy Garante, Sep 2023 | Art. 5, 24. Inaccurate data used for contracts. No change reported. |
| 49 | Uber | 10.00 | Netherlands AP, Dec 2023 | Art. 12, 13. Poor access-request transparency. Appealed. |
| 50 | TIM | 9.52 | Italy Garante, Jul 2026 | Art. 5, 6, 7, 15, 22, 24, 25, 28, 32. Telemarketing via spoofed numbers. No change reported. |
Two fines are left out on purpose. Amazon’s EUR 746 million fine from Luxembourg was annulled on 12 March 2026, and the CMS Enforcement Tracker now records its amount as zero. OpenAI’s EUR 15 million fine from Italy’s Garante was annulled by the Court of Rome on 18 March 2026 on jurisdictional grounds. Both are covered in the appeals section below.
Figure 2: GDPR fines ranked 6th through 10th by amount. Source: DPC Ireland, Dutch Autoriteit Persoonsgegevens, CMS Enforcement Tracker, checked 13 November 2026.
One-line takeaway: the cut-off for the top 50 is EUR 9.5 million, which is less than 1% of the record.
How much are the biggest GDPR fines worth in total?
The 50 biggest GDPR fines add up to about EUR 7.0 billion. The CMS Enforcement Tracker lists 3,417 enforcement actions worth EUR 7.59 billion in total as of 13 November 2026, so the top 50 are roughly 92% of all the money. The top 10 alone are worth EUR 4.96 billion, about 65%, and the top 5 are worth EUR 3.36 billion.
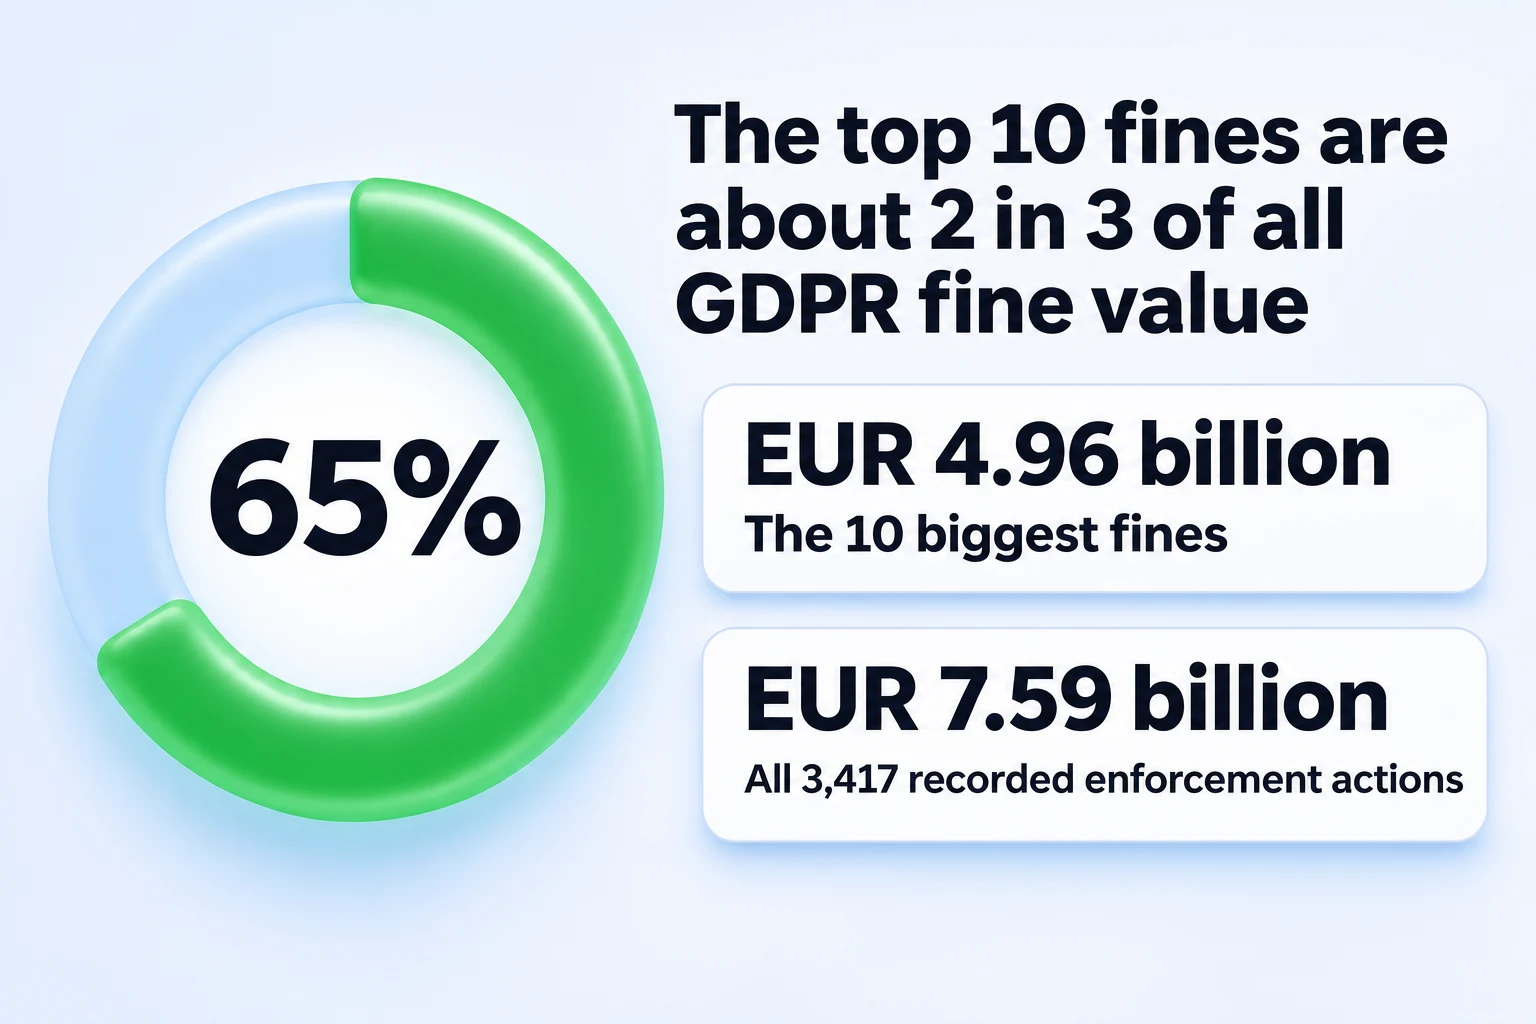
The total has moved fast. Our earlier snapshot of the tracker showed EUR 6.31 billion across 3,202 actions, and the CMS report’s own cumulative figure was EUR 6.11 billion across 2,685 cases. Different trackers count different cut-off dates: DLA Piper’s January 2026 survey put cumulative fines at roughly EUR 7.1 billion. The ranking in this post does not depend on which total you prefer, because every fine on the list is individually sourced. If your site handles EU user data and has not reviewed its legal basis for advertising or its transfer mechanism since 2023, you can generate a GDPR-ready privacy policy that documents legal basis, retention and transfer safeguards. For the wider averages and year-over-year counts, see our GDPR fines statistics breakdown.
One-line takeaway: 50 decisions hold about 92% of the value, so the long tail of small fines barely moves the total.
Which companies have the most big GDPR fines?
Meta and its subsidiaries are on the list 9 times, worth about EUR 2.9 billion. That count includes the four top-10 fines (EUR 1.2 billion, Instagram EUR 405 million, EUR 390 million and EUR 265 million) plus a EUR 251 million breach fine, WhatsApp’s EUR 225 million, a EUR 91 million password-storage fine, Facebook Ireland’s EUR 60 million CNIL cookie fine and a EUR 17 million breach-notification fine.
Uber follows with 3 fines worth about EUR 1.12 billion, and Google has 7 fines worth about EUR 938 million, spread across the Irish DPC, France’s CNIL and Spain’s AEPD. TikTok has 3 worth about EUR 890 million. LinkedIn appears once with EUR 310 million, and Clearview AI appears 4 times for about EUR 90.5 million, with fines from the Netherlands, Italy, Greece and France. Below the top 20, banks, telecom operators and energy suppliers dominate, mostly over telemarketing and breaches.
All 10 of the biggest fines went to platforms with hundreds of millions of users, which follows from how Article 83 works: the cap is 4% of worldwide annual turnover, so only very large revenue bases produce nine-figure penalties.
Figure 3: Combined value of the top 10 fines grouped by company. Source: DPC Ireland, Dutch Autoriteit Persoonsgegevens, compiled 13 November 2026.
One-line takeaway: five companies account for all of the top 10, and Meta alone accounts for 4 of them.
Which countries and regulators issue the biggest GDPR fines?
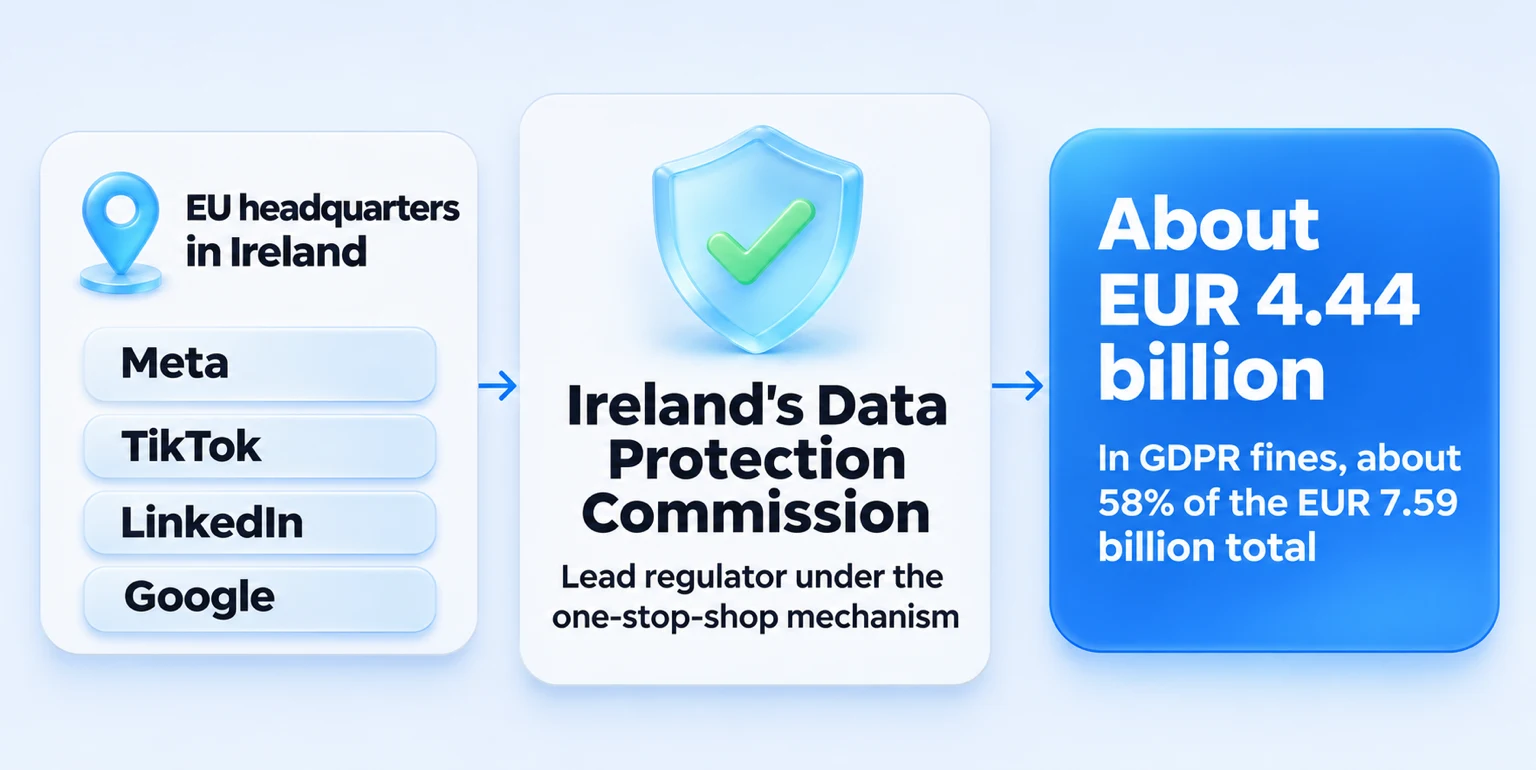
Ireland. The Data Protection Commission issued 8 of the top 10 and 12 of the top 50, worth about EUR 4.43 billion, and the tracker’s total for all 41 Irish fines is EUR 4.44 billion, about 58% of every euro in recorded GDPR fines. The reason is the one-stop-shop mechanism: companies with their EU headquarters in Ireland, including Meta, TikTok, LinkedIn and Google, are regulated by the DPC for the whole EU.
The Netherlands is second with 5 fines worth about EUR 1.26 billion, led by Uber’s two top-10 fines and the EUR 100 million Yango fine. The Dutch regulator is Uber’s lead authority because Uber’s European headquarters are in the Netherlands. France’s CNIL has 12 fines worth about EUR 852 million, mostly cookie and advertising cases against Google, Shein, Facebook and Criteo, which it can fine directly under French e-privacy law without the one-stop-shop route. Italy’s Garante has 9 worth about EUR 225 million, and Germany, the UK, Spain, Greece, Austria and Czechia hold the rest. Country-level detail is in our posts on Ireland, the Netherlands and France.
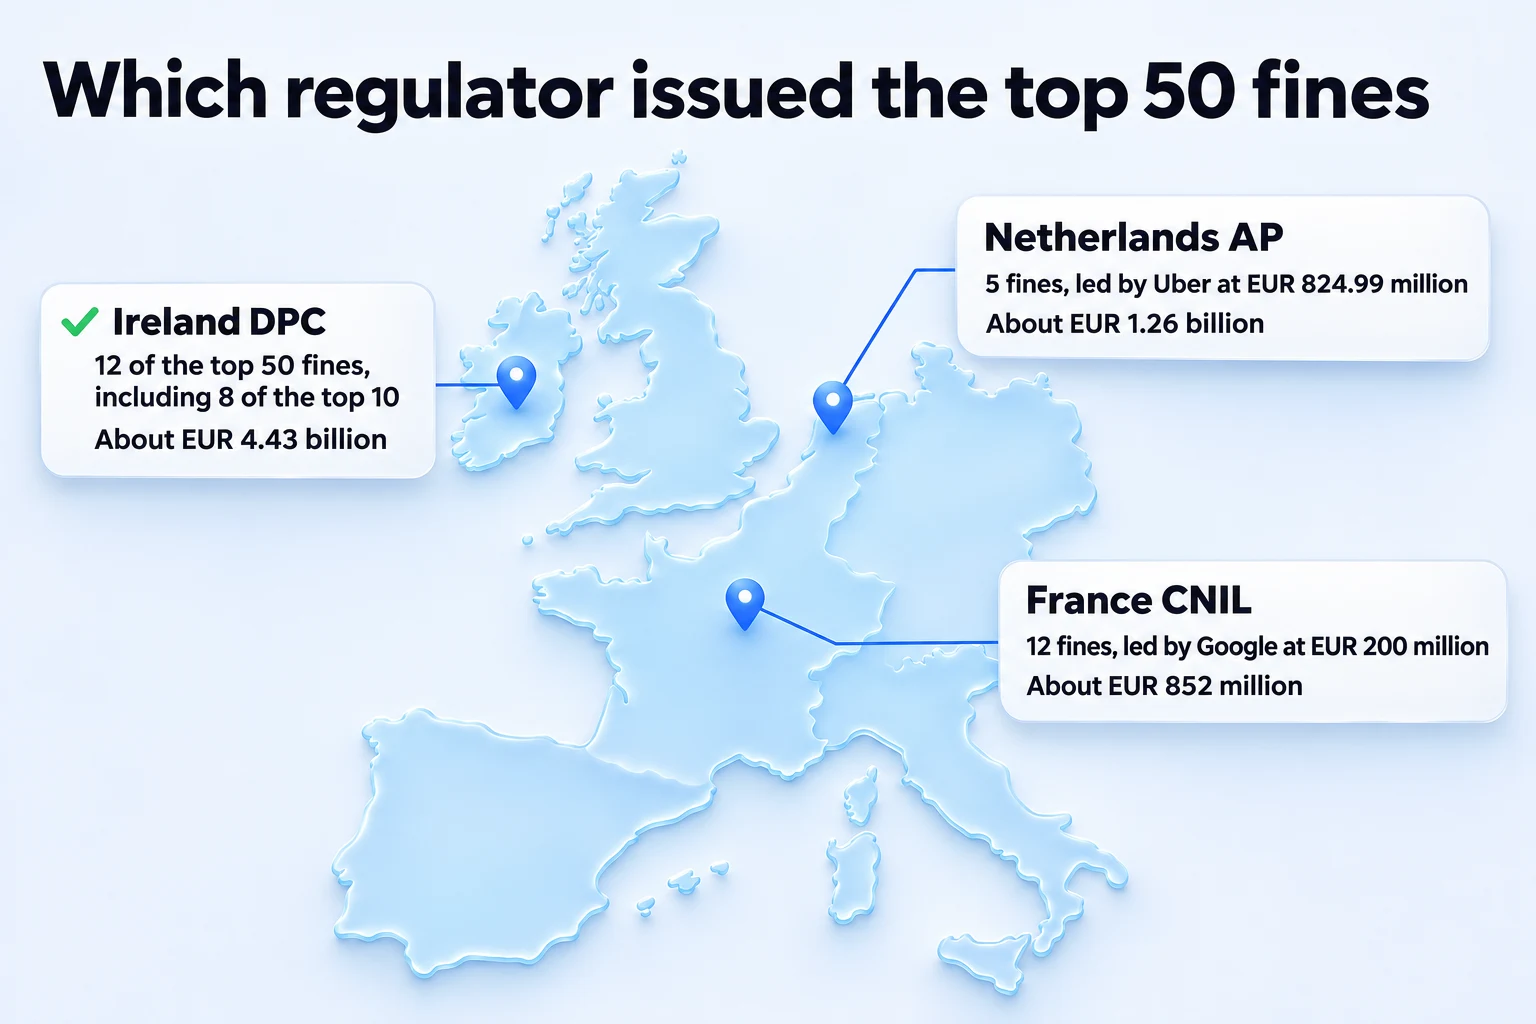
Figure 4: Value of the top 50 fines by regulator. Source: CMS Enforcement Tracker, DPC Ireland, Dutch AP, CNIL, Garante, checked 13 November 2026.
One-line takeaway: fine size follows which regulator has jurisdiction over the largest platforms, not how strictly a country enforces overall.
What were the biggest GDPR fines for?
Five themes explain most of the money. Unlawful data transfers account for 4 fines worth EUR 2.12 billion, led by Meta’s EUR 1.2 billion. Ad tracking, cookies and consent account for 11 fines worth EUR 1.88 billion, which makes it the largest category by count. Transparency and automated decision-making is 3 fines worth EUR 1.06 billion, almost all of it Uber’s 2026 penalty. Security failures and breaches are 10 fines worth EUR 785 million, and children’s data is 4 fines worth EUR 781 million, led by Instagram and TikTok.
| Violation | Fines in top 50 | Combined (EUR M) | Biggest example |
|---|---|---|---|
| Unlawful data transfers | 4 | 2,120 | Meta, 1,200 |
| Ad tracking, cookies and consent | 11 | 1,878 | Google Ireland (location), 403 |
| Transparency and automated decisions | 3 | 1,060 | Uber, 824.99 |
| Security failures and breaches | 10 | 785 | Meta, 265 |
| Children’s data | 4 | 781 | Instagram, 405 |
| Telemarketing | 6 | 155 | Enel Energia, 79.1 |
| Biometrics and facial recognition | 5 | 101 | Clearview AI (Netherlands), 30.5 |
| Other | 7 | 122 | H&M, 35.26 |
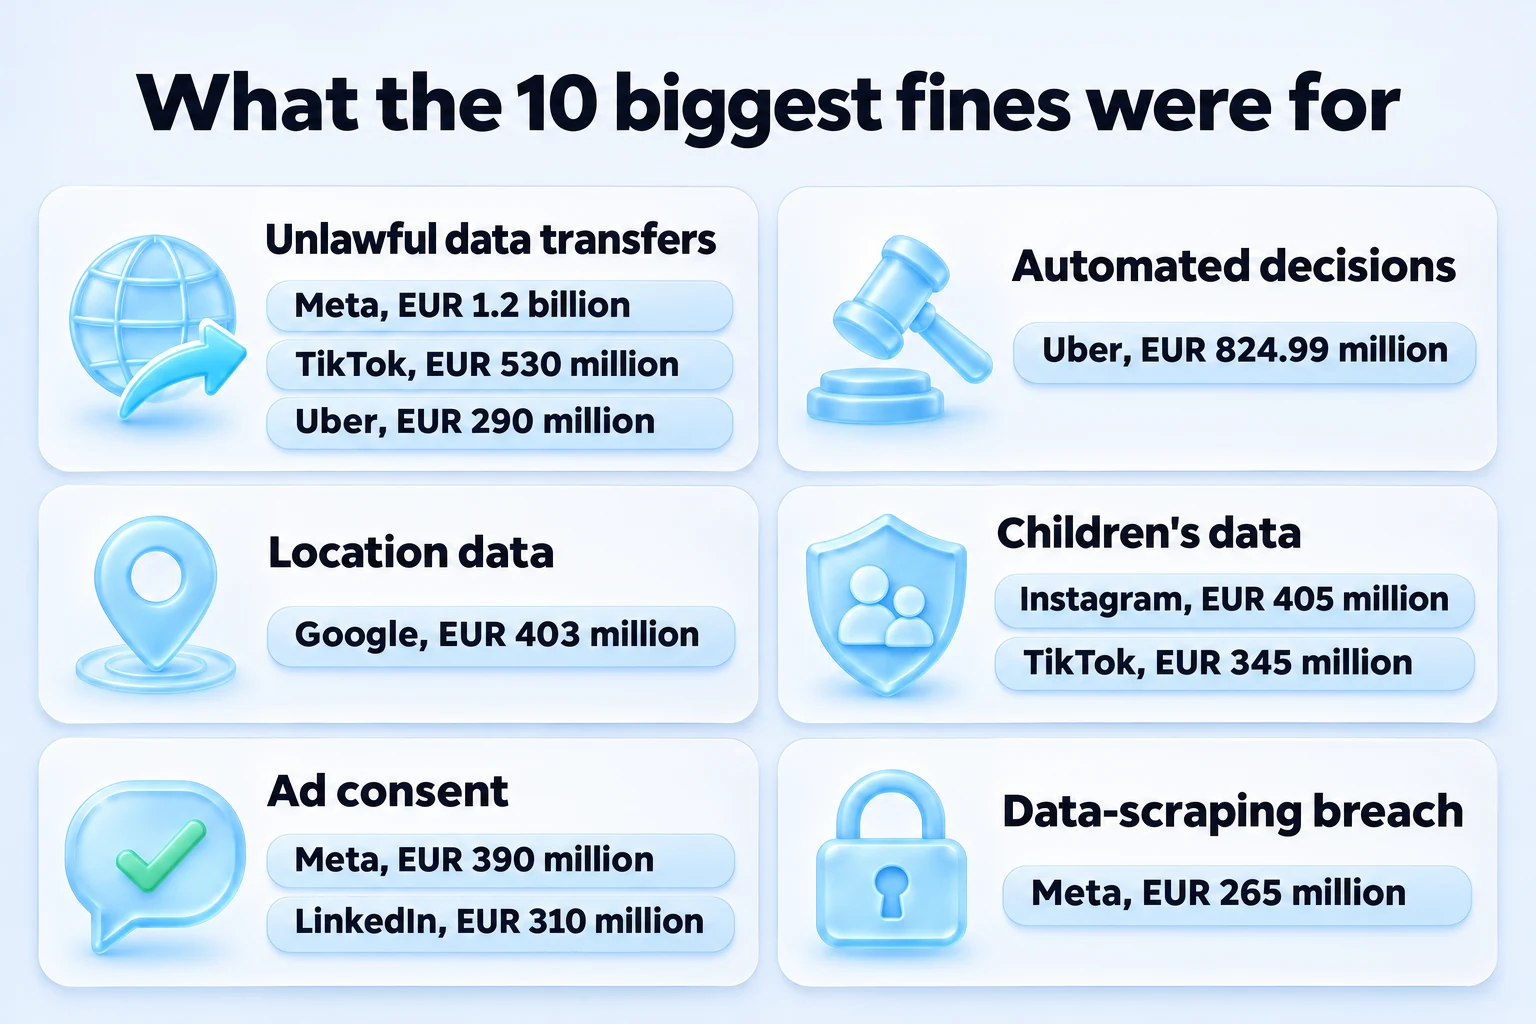
The categories are our own grouping of the primary violation in each decision, and several fines span more than one. The pattern is stable, though: unclear legal basis for advertising, weak transfer safeguards and children’s data keep producing the largest numbers. A current privacy policy and consent flow addresses all three, and our guide to GDPR cookie fines covers the consent cases in more detail.
One-line takeaway: transfers, ad consent and automated decisions make up about EUR 5.06 billion of the EUR 7.0 billion, or roughly 72%.
How have the biggest GDPR fines changed year by year?
Fine value peaked in 2023 at about EUR 2.01 billion across 7 fines in the top 50, driven by Meta’s EUR 1.2 billion record. 2026 is already at EUR 1.46 billion across 10 fines with seven weeks left, which makes it the second-highest year and the one with the most top-50 entries. The earlier years were far smaller: EUR 66 million in 2019, EUR 135 million in 2020, EUR 435 million in 2021 and EUR 757 million in 2022. 2024 and 2025 came in at about EUR 1.08 billion and EUR 1.06 billion.
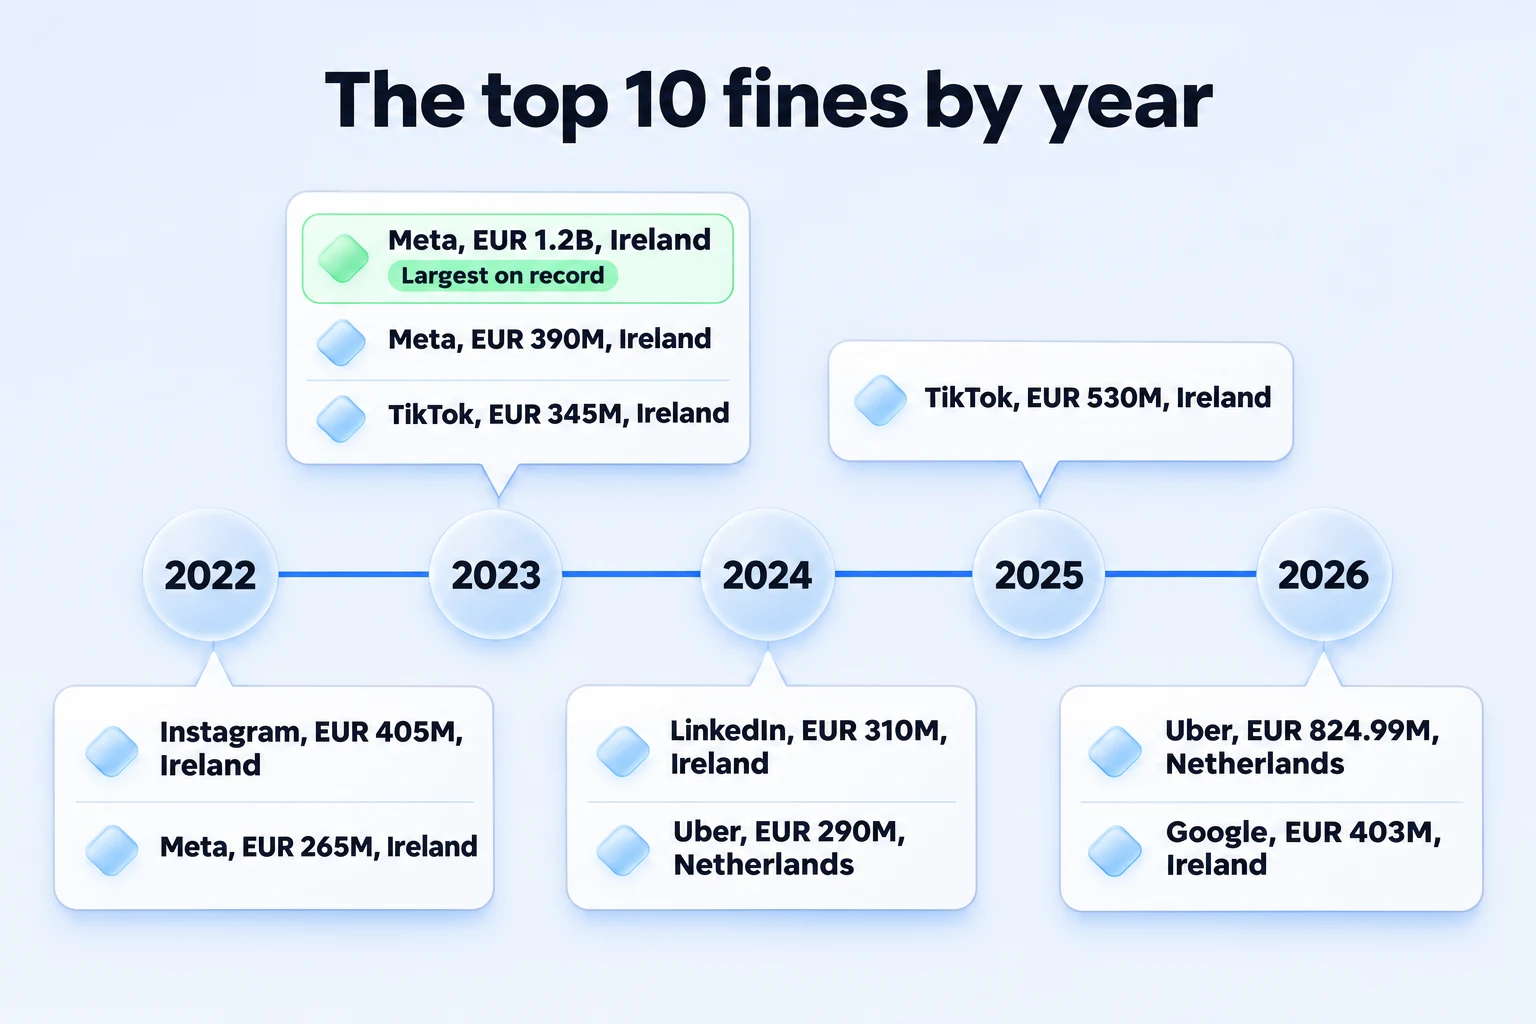
Figure 5: Combined value of the top 50 fines by year the decision was announced, 2026 to date. Source: CMS Enforcement Tracker, regulator announcements, checked 13 November 2026.
One-line takeaway: enforcement against the largest platforms is accelerating rather than fading, with 2 of the 5 biggest fines ever issued in the past three months.
Are the biggest GDPR fines being upheld on appeal?
Most are still being contested, and two have already been undone. The EUR 746 million fine against Amazon, issued by Luxembourg’s CNPD in July 2021 over ad-personalization consent, was annulled by Luxembourg’s Cour administrative on 12 March 2026. The court found the CNPD had not assessed whether the violation was intentional or negligent and had not weighed a milder measure. The underlying breach findings were kept, the case returned to the CNPD, and no new decision had been published as of late October 2026.
The second annulment is OpenAI’s EUR 15 million fine, set aside by the Court of Rome on 18 March 2026 because the Irish DPC had become the lead authority. Amazon France Logistique’s CNIL fine was cut from EUR 32 million to EUR 15 million by France’s Council of State in December 2025, and Austrian Post’s 2019 fine has been cut from EUR 18 million to EUR 16 million and is still not final. Of the largest fines, Meta’s EUR 1.2 billion, TikTok’s EUR 530 million (with a conditional High Court stay granted in November 2025), LinkedIn’s EUR 310 million, Meta’s EUR 265 million and EUR 91 million, both Uber fines and Google’s EUR 403 million (a High Court challenge filed in November 2026) are all under appeal. According to Alliance Risk, about 40% of the roughly EUR 7.1 billion in announced fines was annulled or under challenge as of May 2026. Our GDPR fine appeals post tracks the outcomes case by case.
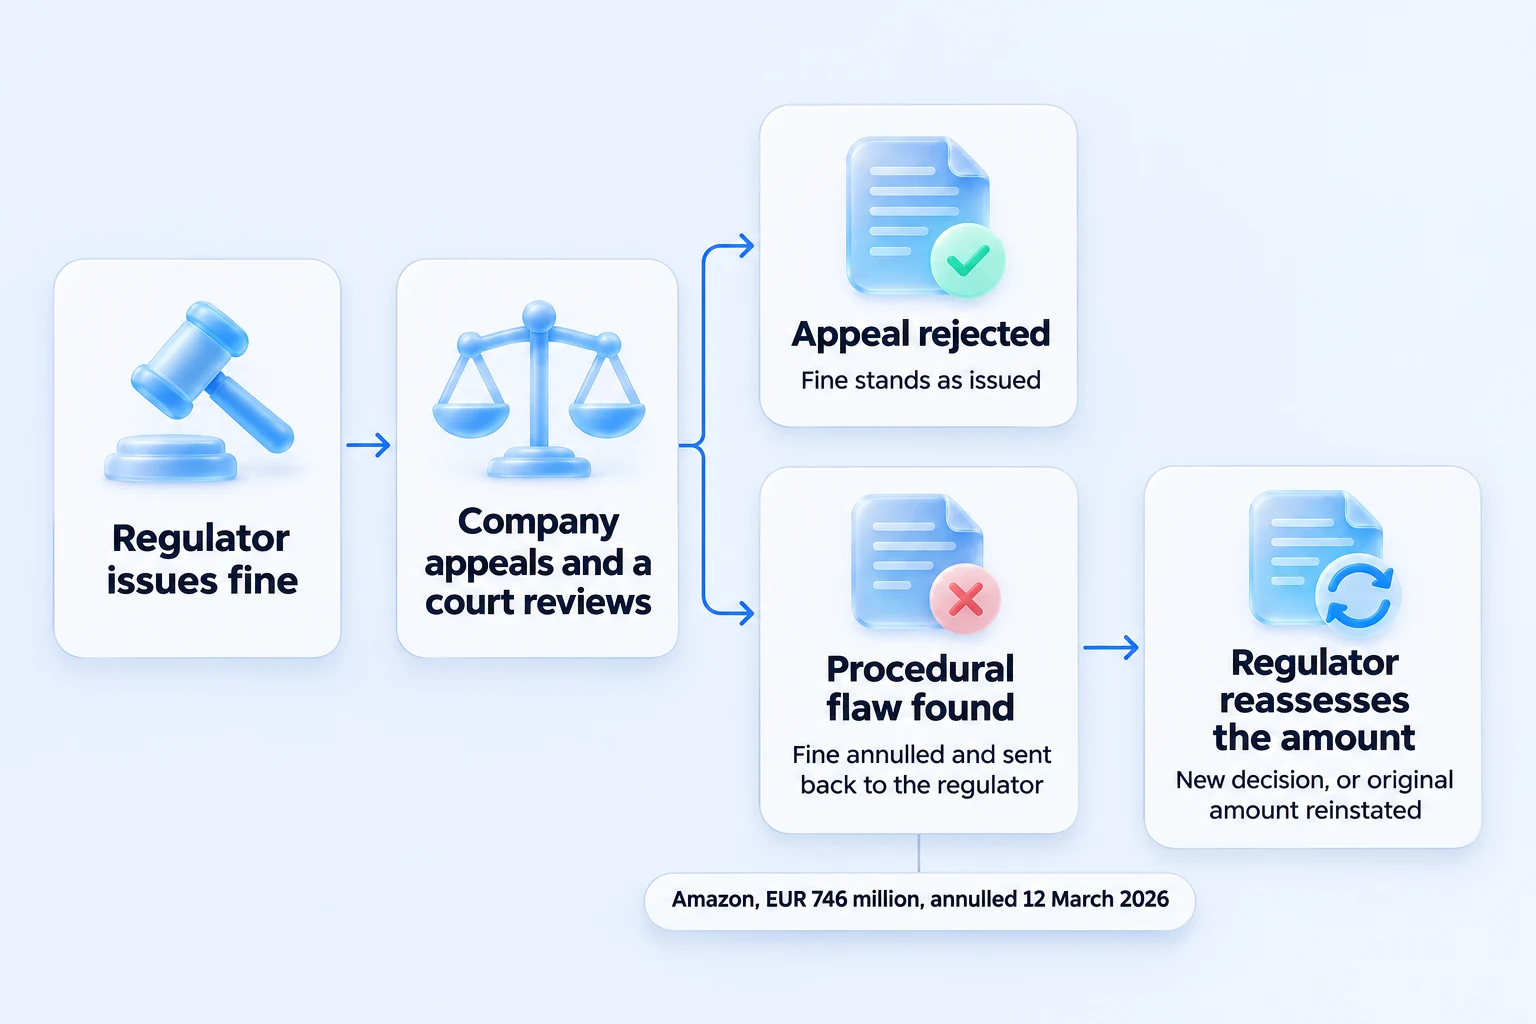
Figure 6: How a contested GDPR fine, like Amazon’s, can be annulled and remanded rather than simply upheld or struck down. Source: Luxembourg Administrative Court ruling, March 2026, as reported by MLex and PPC Land.
One-line takeaway: a fine in this table is a regulator’s decision, not a final bill, and about 2 in 5 euros announced are still being fought or have been undone.
How are GDPR fines calculated?
Article 83 sets two ceilings. The higher tier, which covers breaches of the core principles, consent, data subject rights and international transfers, allows up to EUR 20 million or 4% of worldwide annual turnover, whichever is greater. The lower tier, which covers items such as security of processing, breach notification and records, allows up to EUR 10 million or 2%. Regulators then adjust for the nature and duration of the breach, the number of people affected, intent, cooperation and prior history.
That is why the top of the list belongs to large platforms: 4% of a multibillion-euro revenue base is a nine-figure number, while the same percentage for a mid-size retailer is a few hundred thousand euros. The UK’s fines are issued under the UK GDPR after Brexit and are included because the tracker records them, and their pound figures are shown alongside the converted euro amounts. For what the smallest penalties look like, see the smallest GDPR fines on record.
One-line takeaway: fine size tracks company revenue and breach scale far more than it tracks how serious a smaller company’s violation was.
How was this top 50 built, and where do sources disagree?
Fines are ranked by their current amount in euros, using the CMS Enforcement Tracker as the base (3,417 actions at 13 November 2026) and checking the largest entries against regulator announcements and court reports. Where the tracker and a regulator or court disagree, this list uses the regulator or court figure. Annulled fines are excluded, reduced fines are ranked at the reduced amount, and ties are ordered by date.
The differences worth knowing are these. The tracker records Amazon’s annulled fine as EUR 0, but several lists still rank it second. The tracker shows Austrian Post at EUR 13 million, while the Austrian Federal Administrative Court’s December 2024 decision set EUR 16 million, which is what this list uses. The tracker has no entry for the Garante’s EUR 17.63 million fine on Intesa Sanpaolo from March 2026, which is included from the Garante’s announcement. Dates differ between decision and announcement for many entries, for example Google’s EUR 403 million, which one outlet dates to 16 September and the main reports to 21 September 2026. The Yango fine was recorded against Ridetech International B.V., while reporting says it was levied on its successor MLU B.V. The tracker also lists no articles for Avast. Finally, the tracker does not record every appeal, so “appealed” is set only where a court filing or company statement is reported, and other rows read “No change reported”.
One-line takeaway: the order of the top 10 is not in doubt, but ranks 11 to 50 depend on a few judgment calls that are listed above.
The Bottom Line
The EUR 1.2 billion Meta fine has held the top spot for more than three years, but the list around it changed more in 2026 than in any year since 2023. Uber’s EUR 824.99 million fine and Google’s EUR 403 million fine both landed in the top 10, Amazon’s EUR 746 million fine was annulled and dropped out, and the 50 biggest fines now total about EUR 7.0 billion, or roughly 92% of everything recorded. Ireland’s DPC is behind 8 of the top 10, the Dutch regulator has moved into second place by value, and about 2 in 5 euros announced are still under challenge or already undone. For most sites the more useful signal is the recurring violation behind the money: unlawful data transfers, weak legal basis for advertising and cookies, and children’s data, all of which a current privacy policy and consent flow can directly address. For the fuller enforcement picture beyond the top 50, see our GDPR fines statistics breakdown.
Frequently Asked Questions
What is the biggest GDPR fine of all time? The EUR 1.2 billion fine against Meta Platforms Ireland Limited, issued by Ireland’s Data Protection Commission in May 2023 over EU-to-US data transfers, is the largest GDPR fine on record as of 13 November 2026, per the CMS Enforcement Tracker. Meta has appealed.
What is the second biggest GDPR fine? Uber’s EUR 824.99 million fine from the Dutch Autoriteit Persoonsgegevens, issued in August 2026 over solely automated driver deactivations, is the second biggest. Amazon’s EUR 746 million fine was annulled by Luxembourg’s highest administrative court on 12 March 2026 and is no longer ranked.
How many GDPR fines are worth EUR 100 million or more? Sixteen GDPR fines have reached EUR 100 million or more as of 13 November 2026, from Meta’s EUR 1.2 billion down to the EUR 100 million Dutch fine on the Yango ride-hailing app. Together they are worth about EUR 6.0 billion.
Which company has paid the most in GDPR fines? Meta and its subsidiaries account for 9 of the 50 biggest fines, worth about EUR 2.9 billion combined, followed by Uber at 3 fines worth about EUR 1.12 billion and Google at 7 fines worth about EUR 938 million.
Which country issues the biggest GDPR fines? Ireland. Its Data Protection Commission issued 12 of the 50 biggest fines, worth about EUR 4.43 billion, including 8 of the top 10, because it is the lead regulator for companies with their EU headquarters there under the one-stop-shop mechanism.
Where the Numbers Come From
- enforcementtracker.com. CMS GDPR Enforcement Tracker, live database, 3,417 enforcement actions and EUR 7.59 billion cumulative, checked 13 November 2026. Base data for ranks 1 to 50 except where noted in the method section.
- Per-fine tracker records, in rank order (rank 35 has no tracker entry): #1 #2 #3 #4 #5 #6 #7 #8 #9 #10 #11 #12 #13 #14 #15 #16 #17 #18 #19 #20 #21 #22 #23 #24 #25 #26 #27 #28 #29 #30 #31 #32 #33 #34 #36 #37 #38 #39 #40 #41 #42 #43 #44 #45 #46 #47 #48 #49 #50
- Data Protection Commission Ireland. (2023). “Data Protection Commission Announces Conclusion of Two Inquiries into Meta Ireland.” EUR 1.2 billion fine over EU-US data transfers, 22 May 2023, and EUR 390 million fine, 4 January 2023.
- European Data Protection Board. (2026). “Dutch DPA fines Uber EUR 824,990,000 for unlawful automated decision-making and insufficient information.” Articles 22 and 13, conduct 2018 to 2022, Uber appealed.
- RTE. (2026). “Google fined EUR 403m by Irish watchdog over location data.” DPC decision, 21 September 2026. Appeal reported by The Irish Times, 9 November 2026.
- Data Protection Commission Ireland. (2025). “Irish Data Protection Commission Fines TikTok EUR530 Million.” 2 May 2025.
- Data Protection Commission Ireland. (2022). “Data Protection Commission Announces Decision in Instagram Inquiry.” EUR 405 million fine, 15 September 2022.
- Data Protection Commission Ireland. (2023). “DPC Announces EUR345 Million Fine of TikTok.” 15 September 2023.
- Goodwin Law. (2024). “Irish DPC Fines LinkedIn EUR310M for GDPR Violations.” Decision dated 24 October 2024.
- Autoriteit Persoonsgegevens. (2024). “Dutch DPA Imposes a Fine of 290 Million Euro on Uber.” Unlawful US data transfers, August 2024.
- Data Protection Commission Ireland. (2021). “Data Protection Commission Announces Decision in WhatsApp Inquiry.” EUR 225 million fine, 2 September 2021.
- Federal Commissioner for Data Protection and Freedom of Information. (2025). Press release on the EUR 45 million fine against Vodafone GmbH, June 2025.
- Garante per la protezione dei dati personali. (2026). Decision fining TIM EUR 9,516,000 for telemarketing, announced 31 July 2026.
- PPC Land. (2026). “Italy fined Intesa Sanpaolo EUR 17.6M for profiling 2.4M bank customers.” Garante decision of 12 March 2026, EUR 17,628,000.
- PPC Land. (2026). “Luxembourg court annuls Amazon’s EUR 746M GDPR fine, sends case back to regulator.” Annulled 12 March 2026.
- PPC Land. (2026). “Eight years of GDPR: 40% of the EUR 7.1B in fines annulled or under challenge.” Reports Alliance Risk data of 29 May 2026; OpenAI annulment, Amazon France Logistique reduction, Meta and TikTok appeals.
- PPC Land. (2026). “Italian court kills OpenAI’s EUR15M fine.” Court of Rome, 18 March 2026.
- NL Times. (2026). “Dutch watchdog fines taxi app Yango EUR100 million over alleged data transfers to Russia.” 8 May 2026.
- Vie publique. (2025). CNIL fines against Google (EUR 200 million and EUR 125 million) and Shein (EUR 150 million), September 2025.
- enforcementtracker.com. (2024). Garante decision on Enel Energia, EUR 79.1 million, 8 February 2024.
- IAPP. (2023). “Garante fines utility company 10M euros for using PI to open unsolicited contracts.” Axpo Italia, decision of 28 September 2023, announced 23 October 2023.
- Inside Privacy (Covington). (2026). “Amadeus IT Group receives GDPR fine.” AEPD fine of EUR 18 million, EUR 14.4 million after early payment, made public in May 2026; Amadeus intends to appeal.
- Menorca.info. (2025). AEPD fine of EUR 10,043,002 on Aena for facial recognition without a prior impact assessment, November 2025; Aena says it will challenge it in court.
Note: All figures verified as of 13 November 2026. The list is re-ranked whenever a fine is announced, annulled or reduced and is refreshed at least twice a year. Appeal status reflects court filings and company statements reported by the sources above; the CMS tracker does not record every appeal.